
Editor’s pick · MIT
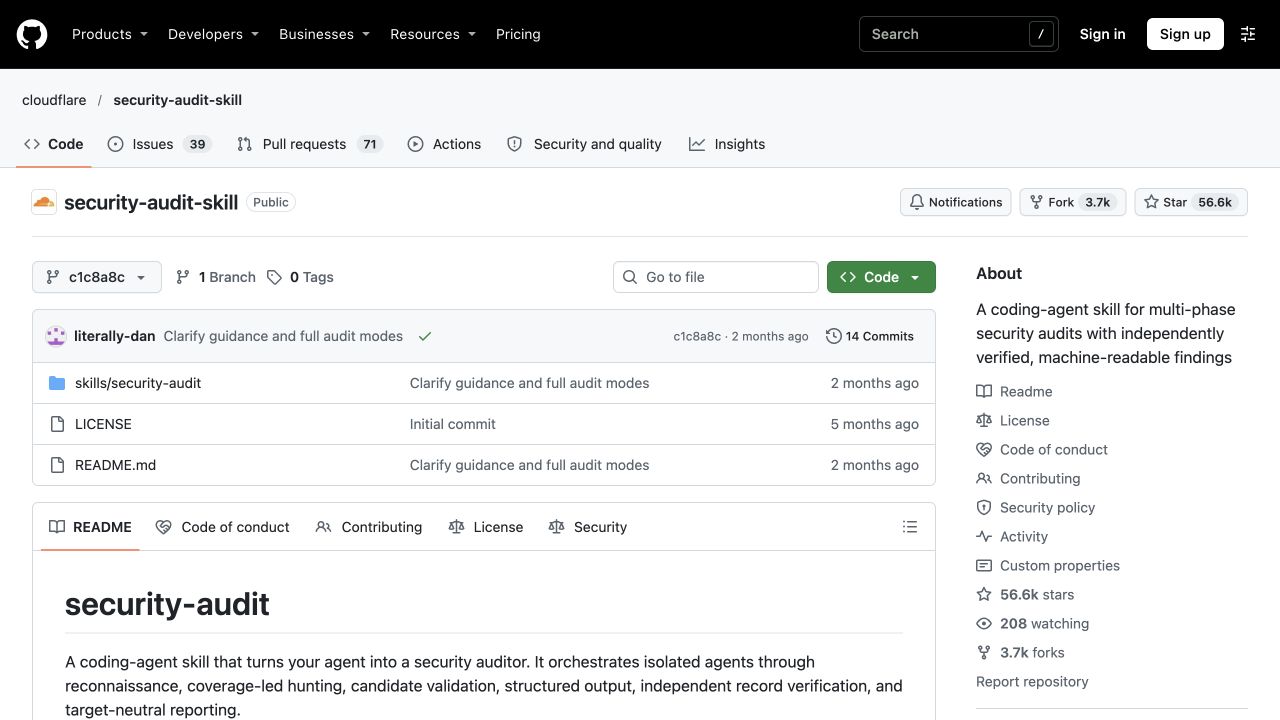
Cloudflare Security Audit Skill
A six-phase workflow for coding agents that maps trust boundaries, tracks audit coverage, hunts for vulnerabilities and sends each candidate to a fresh verifier. It keeps confirmed findings, unresolved leads and rejected candidates distinct, then produces reports from structured records.
View Cloudflare Security Audit Skill repository ↗- Weekly star growth
- +10,069
- Total stars at snapshot
- 56,592
- Useful for
- Security engineers and maintainers who want repeatable evidence and coverage records while using coding agents to inspect a repository.
- Before you try it
- Requires a tool-using model with parallel sub-agents, Node.js for validators, and an OS-enforced sandbox before executing target-controlled code. The sandbox must restrict networking, environment, resource use and writes. Without those controls, unresolved execution evidence stays marked needs_validation. The instructions are MIT-licensed; model service costs are separate. No audit or installation was tested here.
- Latest activity at snapshot
- GitHub weekly Trending observed Nov 2 (UTC); latest source commit Sep 14, 2026. Popularity is not a new software release. Growth is GitHub’s displayed rolling-week figure, not a local seven-day measurement.
- License
- MIT